-
- On October 19, 2026, a his.com customer account was hijacked and used to send phishing spam to a number of his.com addresses.
- This message had the title “You have a New Activity” and claimed that the recipient’s account had been logged into from Russia.
- The message contained a link to “Review Login Activity“. This led to a bogus login page where you were prompted to enter your email address and password. If you were to do this, the bad guys would have your login credentials, and your mailbox would soon be exploited to send spam.
- This is a classic phishing message crafted to look like an official notification from your email provider, containing a bogus notification that your email account had been compromised from another country.
- If you received one of these messages, delete it.
- These messages came from a compromised Amazon Web Services account in California. We have reported this to AWS, and we have reported the link used to harvest email credentials to Google so it can be blocked in Chrome, Firefox, and Edge.
- On October 19, 2026, a his.com customer account was hijacked and used to send phishing spam to a number of his.com addresses.
Zimbra email throughput backlogged Monday, 11/10/25 – Resolved
We’re working on a throughput issue with our upgraded Zimbra system. Incoming email may be delayed. We’ll post an update here when the issue is resolved.
Update 5 PM: the problem was diagnosed and resolved, and mail delivery is now immediate.
Apple iOS 18 – email problems – update to iOS 18.1
We’ve been seeing email problems for some users with iPhones or iPads that have been updated to iOS 18. iOS 18.1, released on 10/28/24, reportedly fixes these bugs.
If you’re using an iPhone or iPad that’s on a version of iOS 18 that’s less than 18.1, you should update now – this should resolve these problems.
Delayed mail to some mailboxes Monday 8/26/2024 – Resolved
Mail to some Zimbra mailboxes was delayed briefly Monday afternoon because of an issue with a mail relay where a redundant failover didn’t work as designed. The issue has been identified and resolved. This affected only some mailboxes, and no mail was lost – the delayed mail was queued and was delivered when the issue was resolved.
Phishing email claiming to be from billing@his.com “Credit Card Status on HIS account”
This morning some of our customers with @his.com or @hers.com email addresses received a phishing email claiming to be from billing@his.com, with a subject line of “Credit Card Status on HIS account”
The text may vary but they look like this:

This message contains a link to a non-HIS web site “asete.info”, where the bad guys hope to harvest your username and password.
This web site should be blocked be any anti-malware app – provided you have one installed.
If you receive email that looks suspicious, don’t click any links in the email. In a case like this one – we did not send this message.
These phishing emails used to be fairly easy to spot but this one is very cleverly crafted to looks like one of ours.
Phishing mail claiming to be from Amazon
We’ve seen phishing mail claiming to be from Amazon, saying that there’s a problem renewing your Amazon Prime membership:

This links to a site in India, where the bad guys hope to harvest your Amazon username and password.
If you receive email that looks suspicious, don’t click any links in the email. In a case like this one, log on to your Amazon account separately (not by clicking the link!) and investigate.
These phishing emails used to be fairly easy to spot because they’d get the graphics wrong or contain mistakes in grammar or spelling, but now the bad guys are using AI to generate the content, and in many cases it looks very real. If you’re using a Mac or PC, hover your mouse cursor over the From: address or the login link to see where they point. This isn’t as easy to do on a phone or tablet.
Phishing mail claiming “multiple billing error”
A his.com customer email account was hijacked and used to send phishing mail to other his.com addresses that claimed to be from error-billing@his.com, asking recipients to log on to “retract the multiple charges”. Following this link would take you to a real-looking copy of a Zimbra email login, where logging in would reveal your password to the bad guys, who would then use your account to send more phishing mail.
The customer whose account was used to send this mail fell for a different phishing email and revealed their password.
This particular email came from an IP number in the UK, but the fake login page it links to was in Turkey.

If you received one of these, delete it.
Phishing mail to his.com addresses from “billing2023@his.com”
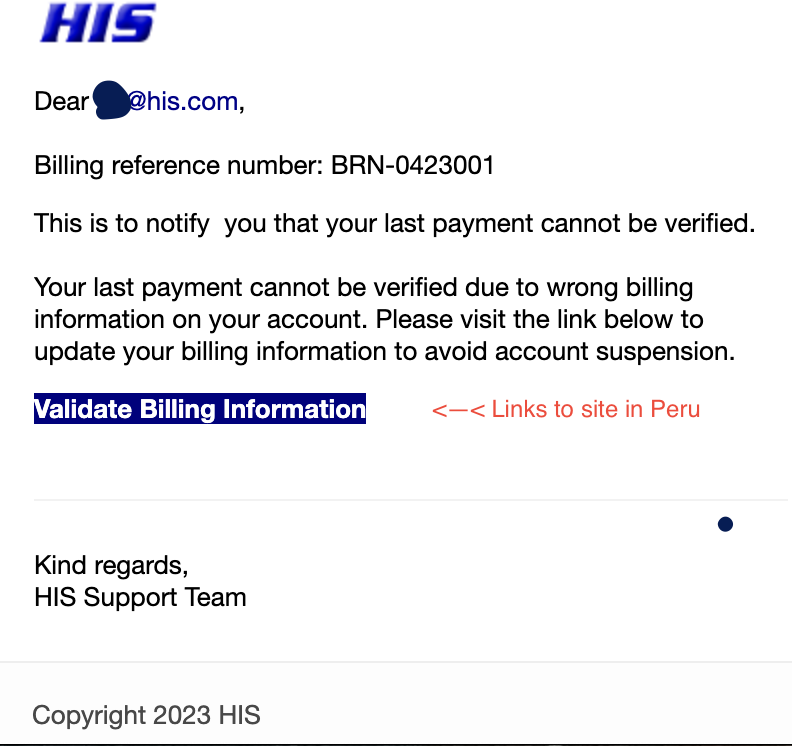
Phishing mail from forged address “billing2023@his.com” was received by some his.com mailboxes today, 11/28/2023. Most phishing messages like this one are blocked by our spam/virus/phishing filters, but some copies of this particular message got through.
The body of the message looks like this, with the HIS logo. The message came from an IP number in Indonesia. The “Validate Billing Information” link connects to a site in Peru. This fake login site is now disabled, but when it was active, the page was designed to look like an official his.com page, and was designed to trick users into entering not just their email addresses and passwords, but credit card and other personal information as well.
If you received this message and haven’t clicked on the links, just delete the message.
If you were tricked into entering your info on this bogus site, change your email password ASAP by logging on to https://webmail.his.com
If you entered your credit card info, call your bank immediately and let them know what happened.
Phishing mail with “Docusign” attachments
We’re seeing quite a few email messages that claim to be about an invoice you haven’t paid and have PDF attachments supposedly from Docusign that you’re supposed to look at. They’ll have subject lines like “Delayed Payment Penalty Notification”. You probably won’t recognize the supposed sender as somebody you do business with, and if you hover your mouse over the From: address in the email you’ll see that the address is from some random domain. The From: addresses are hijacked accounts, and this is a phishing attempt. Most of these gets stopped in our Barracuda spam filters, but there are so many that some are getting through. If you get any of these, delete them.
More information from Docusign: https://www.docusign.com/trust/security/incident-reporting
Spam Filter Glitch 6/5/23 – resolved
At 5:30 PM Monday 6/5/23 one of our vendors glitched and some mail to domains that we host was briefly blocked. That vendor was removed from the mix and the problem has been resolved.